Pages

Showing posts with label privacy. Show all posts

Nov 29, 2010

Open Forum on “Legislative Proposal of Personal Data (Privacy) Ordinance” 個人資料(私隱)條例立法建議” 公開論壇


The Constitutional and Mainland Affairs Bureau (CMAB) has recently published the Report on Public Consultation on Review of the Personal Data (Privacy) Ordinance. We have jointly organize the open forum to let professionals air their views.
Title: Open Forum on "Review of Personal Data (Privacy) Ordinance"
Date: 9-Dec-2010 (Thu)
Time: 7:00pm-9:00pm
Venue: Room 202, Duke of Windsor Social Service Building, No. 15 Hennessy Road, Wanchai.
Language: English and Cantonese
Fee: Free of charge


Co-organizer


The Professional Commons


IT Voice

Internet Society Hong Kong Chapter

Hong Kong Internet Service Providers Association

Hong Kong Information Technology Federation

ISACA China Hong Kong Chapter

Professional Information Security Association

Supporting Organizations

Communications Association of Hong Kong


Association for Computing Machinery - Hong Kong Chapter

Hong Kong Association of Interactive Marketing

IEEE Hong Kong Section Computer Society Chapter

Information Security and Forensics Society


Speakers
  • Ms Adeline Wong (Under Secretary for Constitutional and Mainland Affairs, HKSAR Government)
  • Mr. Henry Chang (Information Technology Advisor, Office of the Privacy Commissioner for Personal Data)
  • Mr. Wilson Lee (Chief Personal Data Officer, Office of the Privacy Commissioner for Personal Data)
  • Mr. Charles Mok, Vice Chairperson (Professional Commons)
  • Mr. Ian Christofis (PISA)
  • Mr. SC Leung (IT Voice)
  • Mr. Lento Yip (Hong Kong Internet Service Providers Association)
  • HKITF representative (HKITF, Hong Kong Information Technology Federation)
Reference: Report on Public Consultation www.cmab.gov.hk/doc/issues/PCPO_report_en.pdf

Feb 26, 2010

雲端運算的新旗艦和私隱的擔憂 —— 談Google公共DNS服務

Google在2009年12月宣布染指DNS服務[1],引起廣泛關注。

Google公共DNS服務是免費的,現在試驗階段祇提供對個人用戶的服務,相信能吸引用戶和中小型企業。Google公共DNS是雲端運算的其中一個層次 —— 基礎設施即服務 (IaaS, Infrastructure as a Service)。雲端運算的特點,是用戶不需要了解「雲端」中基礎設施的細節,不必具有相應的專業知識,也無需直接進行控制,只關注自己真正需要什麼樣的資源以及如何透過網路來得到相應的服務。

個人用戶的DNS伺服器設定,通常指向ISP的DNS伺服器;要使用 Google 公共DNS服務,就得以手動設定,將主要DNS伺服器指向Google公共DNS伺服器的IP地址8.8.8.8或8.8.4.4。(見圖1)


圖1

相較ISP的DNS服務有甚麼特別?

一個網站的內容,無論是文字、圖片及其他多媒體,都可能來自多個來源;入門網站就包括很多外嵌入的內容如股票走勢、天氣慨況、熱點消息和廣告等。所以,個別網頁的下載是涉及從多個來源下載個別的文字和媒體資源。瀏覽器從主網頁知道這些資源的URL後,先要詢問自己ISP的DNS伺服器,URL上的機器名稱(host name)的IP地址是甚麼,ISP的DNS伺服器會代為向資源所授權的DNS伺服器詢問,將回覆轉告用戶,用戶然後向資源的伺服器(的IP地址)發出下載的請求。ISP的DNS伺服器通常會把回覆的資訊放在快取記憶一段時間,方便再有類似查詢,無需重覆再問。

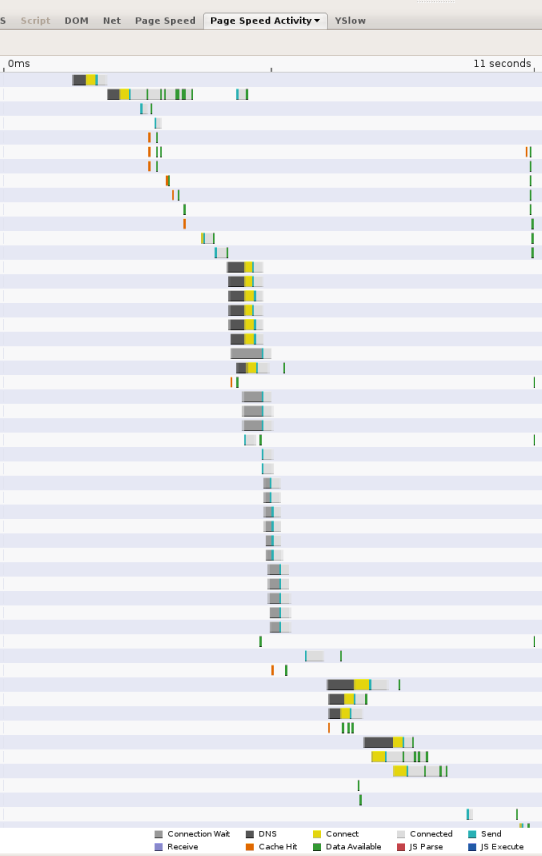
由Google提供的網頁下載時間分析(見圖 2),可以見到DNS查詢(深灰色)對用戶的整個等待時間其實有顯著的影響,在ISP的DNS伺服器的快取記憶無請求的資訊時,是要向外查詢,ISP網絡和外間網絡的網絡距離和頻寬,都直接影響回應的時間。


圖2. Google 提供的網頁下載性能分析

Google利用資訊基建的規模和分散性覆蓋的優勢,提高公共DNS服務的效能和可靠性。透過anycast 技術,同一個DNS伺服器IP位址8.8.8.8,在不同地區是會指向不同的實體伺服器去,「梗有一家在附近」,讓用戶能夠獲得更快捷,更可靠的DNS服務。

一般用戶未必留意到,Google公共DNS服務是支援 IPv6 的,而且設計上對保安的攻擊的抵禦能力較高。記得在12月18日,很多用戶發覺 Twitter.com 網站的模樣完全不同了,還以為是網頁被駭了?原來,被駭的是Twitter的DNS伺服器,駭客透過更改上面的記錄,欺騙用戶到錯誤的IP地址,由此可見DNS保安的重要性。有關Google公共DNS服務的保安分析,可以參考我的博錄(Blog)文章[2],此處不贅。

回到Google公共DNS服務,試想想,若果所有用戶探訪任何網上資源時,都先問Google DNS,那麼Google將掌握甚麼樣的統計數字?造就些甚麼商機?我相信在將來Google會利用DNS提供增值服務,就像OpenDNS一樣,例如,網站市場調查、過濾垃圾電郵來源網域、過濾不安全內容,這些服務對企業應該會很吸引,會成為Google 繼搜尋器之後的另一旗艦。


私隱及服務承諾的問題


公共DNS服務雖然很棒,用戶無需瞭解它內在的複雜性,就可以應用自如。但是,正如其他的雲端運算服務一樣,因為用戶對它的背後的運作概念模糊,又豈能百分百安心呢?

例如,雖然大家都對Google服務的可用性(availability)有一定信心,但還是會問,如何確保服務水平和管理當機時間呢?原來,Google在服務條款中已講明對服務水平沒有任何承諾,還勸喻用戶要設定次要(secondary)DNS伺服器作為後援,指向自己的ISP或內部的DNS伺服器。

至於私隱問題,大家都知道,DNS日誌內記錄的是用戶採訪的網域(domain)足跡和歷史,雖然日誌不記錄網頁的內容,但是「畫公仔唔使畫出腸」吧。Google的私隱政策[3] 說明,他們保存兩套日誌:臨時日誌存儲用戶的完整的IP地址,但祇保留24至48小時;永久保存的日誌有用戶的地理位置和網絡資料,但沒有個人身份或IP地址資料。表面看來,私隱政策已嘗試照顧問題。然而,Google又如何能提供透明度,以確保隱私政策被貫徹執行。再者,在不同的國家,執法機構或部門都可以要求Google繞過私隱政策,提供涉及私隱的資料以配合調查,Google公共DNS不就是網絡的跟蹤器?

那麼,你的個人資料若在香港受到法律保護,但放到「雲」上,又是否受到相同的保護?答案是不。原來,本港《個人資料(私隱)條例》第33節雖然涉及有關個人資料流出境外的監管,可是現時還未立法,為跨境因為提供的保護。

隨著世界不斷邁向網絡社會,電子商貿日趨發達,個人私隱資料洩漏的風險正以級數上升,一些國家已自行立法,或依據《歐盟數據保護指令》和《歐洲委員會公約》第108條立法,監管跨境的個人私隱資料。2009年11月,全球40多個國家的100個以上的民間組織和關注私隱權的專家,發起《馬德里宣言》[4],呼籲國際社會正視私隱的問題,更具體提到未符合《歐洲委員會公約》第108條的國家應從速立法。我和IT呼聲的朋友,就《個人資料(私隱)條例》諮詢提交意見書[5]之中,就敦促香港政府早日為33節立法。 世界上的私隱保障條例還未到位的一天, 公用的雲端運算服務,如Google公共DNS服務的私隱問題,始終是個隱憂。

作者:梁兆昌
本文見於 《PC3 Corporate 2010 Mar》

Dec 5, 2009

Google Public DNS -Security & Privacy Analysis

Author: S.C. Leung
Google announced provision of free Google Public DNS service [1]. It is now in experimental stage targeting individual user only. Google Public DNS service is part of Google's cloud computing initiative to make Internet services available anywhere at any time.

It has a far reaching impact to the Internet after Google goes into the search engine business. Here is my preliminary analysis from information security & privacy perspective.

Performance and Availability
With the vast and distributed points of presence, clients are able to obtain more speedy and more resilient DNS services via geo-location awareness load balancing (technically using anycast), cache and prefetch name resolution. [2]

Comments: Just as the GMail service, Google has a wonderful resilience in infrastructure that corporations cannot generally afford. However, Google has no commitment on service level and you are always advised to have a secondary DNS pointing to your own ISP or internal DNS server.

Security
Google Public DNS has designs against spoof attacks leading to DNS cache poisoning. [3]
  • filter out malformed queries and responses.
  • use more randomness of source ports and responding DNS servers
  • randomly vary the case of letters in domain names queried by "0x20 technique" [4] to reduce chance of spoofed response.
  • remove duplicate name queries are removed to mitigate birthday attacks (spoofed flooding response to increase chance of hit)
Google Public DNS has designs against Denial-of-service (DoS) and amplification attacks [3]
  • rate limiting of outgoing queries to name servers
  • rate limiting of outgoing responses to clients
Comments: These security measures are very carefully designed to combat the most current DNS attacks. Note that, however, there is a limitation in Public DNS. It can only accept and forward DNSSEC requests but CANNOT validate DNSSEC responses. When DNSSEC is popularizing we need to keep an eye on this.


Privacy
Everyone knows that a log of you DNS queries is merely the same as a log of your web access habit without the content involved. Another Google service Safe Browsing was challenged by a researcher RSnake of potentially infringe clients' privacy by collecting client machines' browsing history[5]. Will that happen to Public DNS? What does Google log?

The Privacy Policy [6] specifies that they stores two sets of logs: temporary and permanent. Temporary logs (kept within 24-48 hours) store the user's full IP address so that Google can spot potentially bad things like attacks and fix problems like particular domains not showing up for specific users. The permanent log has no personally identifiable information or IP information but user's geolocation and ISP (AS number). Google will not correlate user's use of other services, like Search and advertisement.

Comments: The Google privacy policy has looked into the privacy concerns properly. However, as in cloud computing, how can they provide the transparency to assure the privacy policy is followed closely. Secondly, we also need to take into account the overriding conditions that may apply if Google is asked to cooperate with law enforcement agencies or authorities. Google not only keep track of everything you search, but every address you are visiting. Depending on which country you live in, government agencies have various powers to compel online service providers, such as Google and your ISP, to give them whatever information they might have about your identity and activities. For US, the post-9/11 Patriot Act made it easier for law enforcement agencies to get this information. Other governments will learn to get have access to such widespread surveillance powers for reasons they see fit. [7]


Other Comments


1. We need to be aware that DNS server is a key infrastructure for the directory of information on the Internet. Controlling DNS can directly control information access. Moreover, if a client cannot access an information repository, he has no knowledge if that information repository is unavailable or the name resolution is denied by the DNS server. So a key for freedom of information access is to guarantee that Google does not implement any kind of filtering without user authorization. Google has acknowledged this [1] but should have more transparency on this.

2. As with Google's Safe Browsing service, Public DNS can be used to filter against malware and phishing. It could be a future revenue stream, like Google's competitor OpenDNS. Besides, similar technology can be applied to pornography and gambling filtering for parental care. Once filtering is added, we have to look at how these services could impact freedom of information access and privacy.

3. Fast flux DNS technology is widely used by botnets to provide dynamic DNS resolution of malicious web sites to evade investigation. With Public DNS, Google can play an active role in malware and botnet detection through analysis of the DNS server responses. The information would be very useful for the security community.

4. Last by not least, I like to point out the importance of diversity as commented by the CEO of OpenDNS[8]. From Chrome OS at the bottom, to Chrome browser, and to Google Search at the top, Google is running the end-to-end infrastructure. Google is the largest advertising company in the world. Do we want Google to keep control over so much of our Internet experience? How can we preserve a heterogeneous Internet with lots of parties collaborating to make this thing work.


Back to Top

Reference:

[1] Google Gets Into The DNS Business. Here’s What That Means"
http://www.techcrunch.com/2009/12/03/google-dns-opendns/

[2] Google Public DNS: Performance Benefits
http://code.google.com/speed/public-dns/docs/performance.html

[3] Google Public DNS: Security Benefits
http://code.google.com/speed/public-dns/docs/security.html

[4] Use of Bit 0x20 in DNS Labels to Improve Transaction Identity
http://tools.ietf.org/html/draft-vixie-dnsext-dns0x20-00

[5] Google Safe Browsing Feature Could Compromise Privacy
http://www.darkreading.com/security/privacy/showArticle.jhtml?articleID=218800199

[6] Google Public DNS: Privacy Policy
http://code.google.com/speed/public-dns/privacy.html

[7] You Have Zero Privacy Anyway -- Get Over It
http://www.osnews.com/story/22603/You_Have_Zero_Privacy_Anyway_--_Get_Over_It/

[8] Some thoughts on Google DNS, by David Ulevitch, Founder of OpenDNS
http://blog.opendns.com/2009/12/03/opendns-google-dns/

Feb 4, 2009

一支下籤

剛晉身行政會議的新界鄉議局主席劉皇發,在沙田車公廟為香港求得一支下籤,引為新聞。

其實籤文在2008年在資安已經應驗了。

君不須防人漏料
眼前駭客皆為妖
資安徒把長城築
用戶疏忽禍自招


宜 : 資安教育
忌 : 導人迷信


[Note: this Chinese email is about a modified "oracle saying" stem from the recent news of fortune advice come from the oracle Mr. Lau Wong Fat, the newly appointed Government EXCO member. If you want more explanation please email me]

2006
- IPCC 警監會 cases leaked on web
- LCSD 康文署 leaked citizen records
- Some banks lost data tapes with customer data on it
:
:
2008
- Hospitals leaked patient records via USB
- A bank lost a server with customer information inside
- A bank lost CCTV data tapes with recordings on them
- Some service providers leaked customer data on web site
- Many more ...

Nov 15, 2008

社交網絡有多安全? (How Secure are Social Networking Websites?)

How Secure are Social Networking Websites?
梁兆昌
(載於 PC3 Corporate 2008年10月號)

互聯網技術的新趨勢 Web 2.0,是講求網絡使用者之間的互動。而Web 2.0眾多服務當中,尤其以社交網絡網站(Social Networking Site, 或SNS)帶領了浪潮。根據Alexa.com 網站的調查,十大最受歡迎網站中,SNS網站已佔了四個。至於在香港較流行的,則非Facebook莫屬;無論是企業的行政總裁,又或者是公司的小職員,也可能是FB的使用者。可見,今天的互聯網已從傳統的純以資訊為本的網絡,發展為可建立和維繫友儕社交關係的人際為本的網絡。


他山之(私)隱 可創商機

SNS的熱潮,造就了新一個網絡商機,這個商業模式的成功是建基於用戶群的數量,SNS抓緊人的本性中的「追求自我」和「與人溝通」這兩個本能,這些SNS的設計,就設法讓使用者能夠表達自己獨有的、個性化的一面,猶如踏進別人睡房的私人空間,參觀他的擺設、品味,瀏覽他的私人照片,甚或他的日記。SNS又讓使用者能與朋友無分國界、時區,彼此緊密連繫、互相學習,在互動中創造出新的文化,故此SNS使用者較少拒絕交友請求,讓SNS如潮水般湧進不同的使用者的生活中。最近,一些擁有龐大的用戶群的SNS網站,紛紛獲傳統大企業的青睞,入股注資,分一杯羹。

一些SNS系統,例如Facebook更開放應用程式介面(API),讓不同的軟件開發商和個人參與應用的創作,讓用戶可以隨意安裝自己喜愛的應用程式,既增加其對用戶的吸引力,也為軟件開發商以至用電子商貿作產品服務推廣的企業創造發揮和宣傳機會。此外,由於各SNS互不兼容,又再創造出無數新的商機,不少SNS整合工具 (aggregators)應運而生,為活躍於不同SNS用戶提供方便。


關注SNS的保安問題

然而,一張刀子是沒有兩邊利的 – 要參與這些好玩有趣的SNS,用戶先要乖乖奉上他們的個人資料和私隱。個人履歷和資訊,如姓名、照片、生日、學校、身在的城市、所屬的公司、組織、參加過的活動,以至性傾向和婚姻狀況等私隱,會毫無遮掩地和「朋友」分享,曾經有不法分子利用FB上得到的用戶個人資料進行詐騙。此外,Facebook有眾多類別的應用程式,例如游戲、交談、照片和其他可愛的小玩意等,卻獨欠缺資料保安和私隱的應用程式。Zombies、Vampire和 Hot potatoes是其中幾個較多用戶使用的應用程式,雖然名字看似電腦病毒,其實都是被扣上了人性的Facebook交友工具:被咬者會咬其他人,又或反咬;接到熱薯仔的又會急不及待的交往下一個「傻仔」的手;至於浪漫的點子,就是被擁抱的會擁抱其他人。就這樣,不同的得意有趣的應用就像是電腦病毒般狂野地擴散開去。不過,沒有人會留意到個人資料可能毫無保留地送到應用發展商的手中,宣揚出去。現在是時候數一數自己有多少個交友工具了。


SNS私隱危機越揭越多

以Facebook的應用程式為例,它的特別之處是跨網點應用(Cross site application),即應用程式可以在應用發展商的伺服器運行,但在資料輸出方面,卻在FB用戶的網頁上顯示。在Facebook平台下,使用者對應用程式的保安控制的模式,並不如一般運作系統可以設有防火牆、防毒軟件、私隱保護軟件等防禦工具,而只是當使用者在初始設定應用軟件時,回答幾個簡單的是非題。因此,儘管SNS設有數據存取控制機制,但由於沒有細緻的分級,加上幾乎所有應用程式均要求存取使用者個人資料,使用者可說是無從選擇下開放存取控制。使用者對應用發展商如何貯存和使用他的個人資料,更是無能為力。

五萬名Facebook用戶聯名抗議Facebook的Beacon 廣告系統洩漏用戶資料,事件逼使Facebook CEO向媒體道歉,承認用戶除非事先拒絶,否則無論當使用者登入還是已登出Facebook網站,Beacon系統也會追踪Facebook用戶瀏覽網站和網上購物的紀錄,並把資料自動傳送至Facebook的系統,再向使用者的朋友發出「通報 」。現時電子商貿盛行,不少企業管理人員都會透過互聯網搜集商業資訊和為公司採購物料,要是當中有Facebook的使用者,但他們的紀錄卻因Facebook輾轉外洩予第三者,後果真的不堪設想了。


遵守SNS的最佳保安守則

沒有人希望自己的個人資料在毫無保障的情況下被公諸於世。畢竟個人資料和私隱本身也是個人資產,若這些寶貴的資料甚式個人身份被他人竊取或盜用,後果實在非同小可。因此,SNS用戶必須先了解SNS服務網站和應用程式的運作和存取模式,才能保障自已個人資料的安全。

網絡上數以萬計的Facebook用戶,當中又有多少注意到此類服務可有損私隱?為了喚起網民、企業管理層、政策制訂者、SNS服務提供者對SNS保安的關注,歐洲網絡及資訊保安組織European Network and Information Security Agency (ENISA) 於十月推出一份關於SNS保安問題和建議的諮詢文件,探討包括第三方可下載和貯存網上SNS 使用者資料、SNS上濫發訊息、面孔(影像)辨析和照片標籤(摩登點相)等各類型SNS服務和應用程式所潛在的資訊保安問題,並提出一系列技術和政策建議。

該組織提出的分析和建議極具參考價值,但要政策制訂者又或SNS服務提供者採納和落實,相信不是一朝一夕可以辦到的事。因此,SNS使用者還是加倍注意自己使用SNS的習慣,以及遵守使用SNS的最佳保安守則 (見附表),才能在保障私隱的大前題下,玩得開心和稱心!


使用SNS的最佳保安守則
  • 使用安全密碼防止帳戶被盜用
  • 上傳生活照片、影像時,要留意其他人(包括陌生人)也可能看見
  • 不要發放敏感的資料 (No Disclosure)
  • 不要隨便安裝應用軟件 (Malware avoidance)
  • 調校你的FB私隱存取設定 (Access Control)
    1. 控制誰可以觀看你的履曆
    2. 決定誰人可搜查得到你
    3. 控制發布你的活動資料的內容(News feed and mini-feed)
    4. 控制和你的有交往的人的情報交換
    5. 控制那些應用程式可以存取
    6. 和你的有交往的情報交換